Santa Cruz de la Sierra, Bolivia

Vinicius

I design backend and web logic (APIs, auth, domain), low-level C++20, reverse engineering, and offensive/defensive security. CEO of Mercav.lat. If the service must hold and close cleanly, I am who you want on the call.

About Me

I am Vinicius, 19, living in Santa Cruz de la Sierra, Bolivia. I build backend and web logic end to end — HTTP contracts, business rules, authn/authz, data — and I also read systems at a low level and security. Three axes of the day: serious technology, offensive and defensive cybersecurity, and Jewish halakha as a practical standard. I am not a one-tool niche: I design the service, harden it, and understand how it breaks.

Craft

I start from how a program holds state, talks on the network, and defends itself. In backend and web logic I design APIs, data models, sessions/JWT as contracts, jobs, and observability. In C++20 and RE I work memory, binaries, and overlays that must stay stable under load. On offense I map real failures on endpoints and surface; on defense I close the same path with controls, integrity, and telemetry. I also read markets and chain. Grey-hat here means studying offense to design defense — not publishing recipes.

I design the service. I test it. I close it.
Yahadut

בעזרת השם, כל עכבה לטובה.

In Santa Cruz de la Sierra, learning and the practice of halakha are not a footer. They are the other standard of the same day. Halakha sets the rhythm; the craft is measured with the same seriousness. בעזרת השם, כל עכבה לטובה — every delay is for the good.

Keep scrolling

Work

01

Services and domain

Backend and web logic

I design and ship backend: HTTP contracts, business rules, authentication and authorization, persistence, and clear layer boundaries. Web logic is not empty CRUD: it is the system that must be correct under load and under abuse.

github.com/invertilo
Backend and web logic
02

Endpoints and surface

API security

I review APIs and endpoints as attack and defense surface: authn/authz, poorly scoped objects, flow abuse, secrets, rate limits, and trust chains. I document the failure and the fix — not an exploitation playbook.

github.com/invertilo
API security
03

Security research

Offense and defense

Both sides of the same problem. Offense: surface, logic, and binaries to see where a system yields. Defense: controls, integrity, and telemetry so that path stops being usable. Blind defense does not work.

github.com/invertilo
Offense and defense
04

Role

Mercav.lat

CEO. The product lives at mercav.lat; here, the role and the link. The rest of the site speaks to the technical craft.

mercav.lat
Mercav logo: gold monogram on black

Let's talk

GitHub activity

invertilo — the rhythm of the craft, not just the README

Audit and incident response

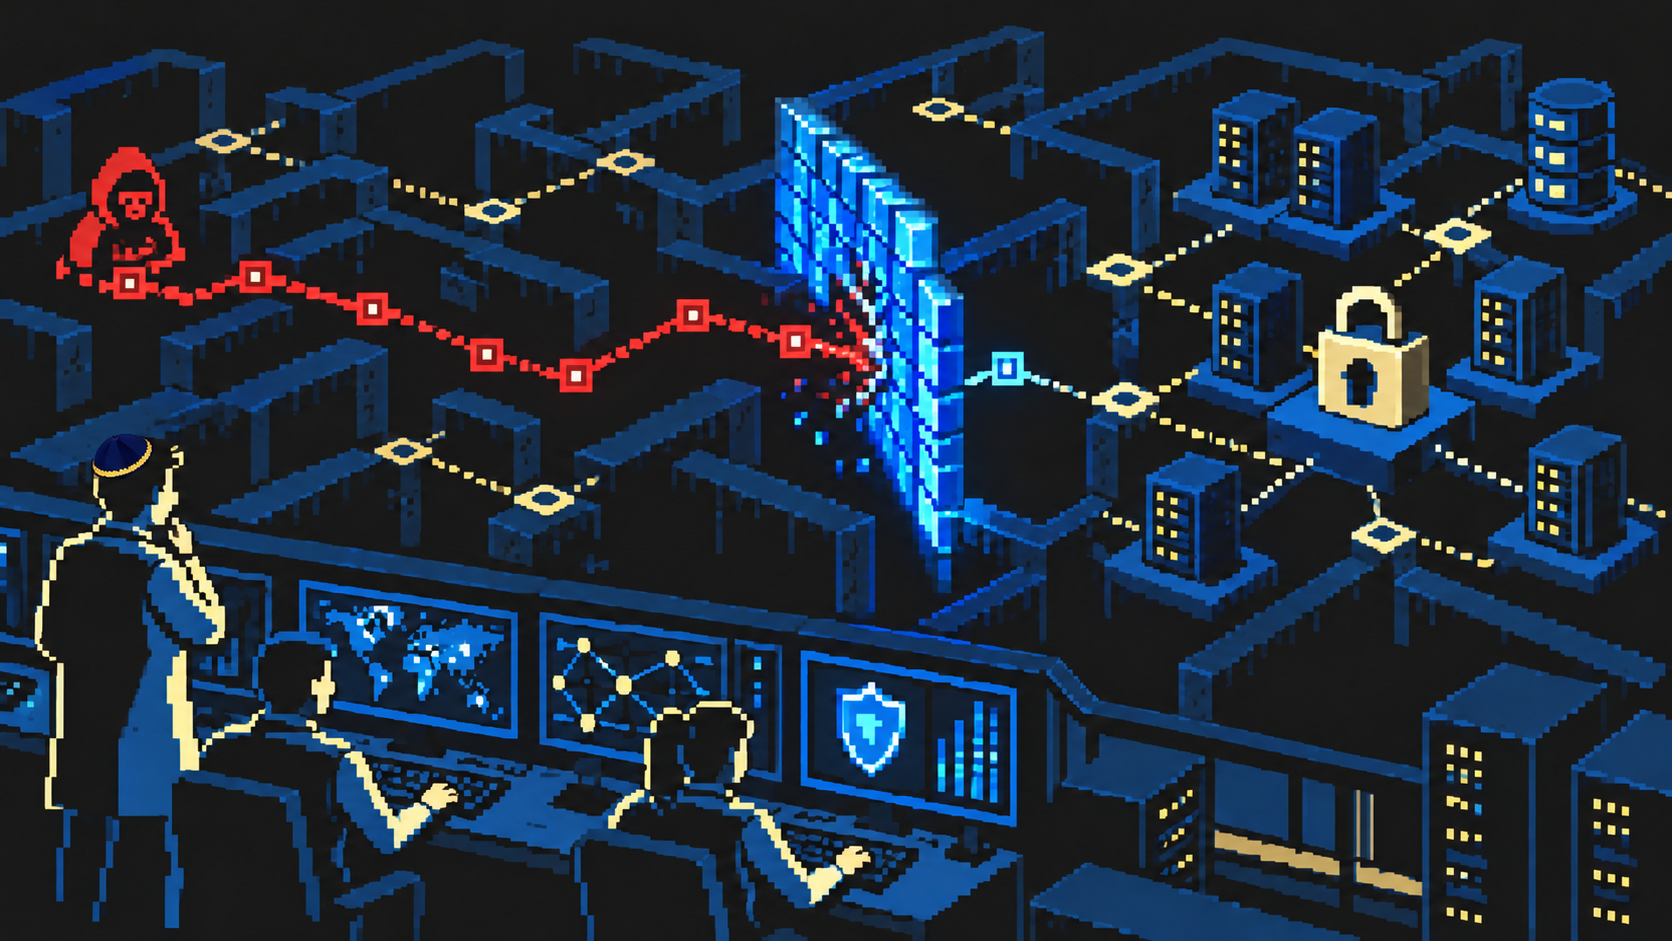
When an attack already happened — or when you need to show how entry would have worked — I reconstruct the path: vector, observed methods, endpoints touched, data at risk, and what to close. An actionable report, not an exploitation playbook.

Illustrative case (anonymous)

API with poorly scoped object access

Reconstruction of a typical REST API incident: an actor abused a predictable identifier and an export endpoint with incomplete authz. Not a real client; this is the report format I deliver.

Risk range. High to critical — multi-tenant exposure of personal data and bulk extraction via export.

Read the report

If you need an audit or post-incident response — we should talk. Connect

Connect

If you need someone who designs the service, hardens it, and understands how it breaks — we should talk. In earnest.

Backend, web logic, low-level systems, and security: one profile that closes the loop. If we talk, we talk in earnest.

Frequently asked questions